Understanding the Penalty Structure Under Schedule 1
Unlike earlier drafts of Indian privacy legislation that linked fines to global turnover (as in the EU GDPR's 4% cap), the DPDP Act 2023 introduces
fixed per-violation statutory ceilings that reach up to
₹250 crore.
These fines are directly adjudicated by the
Data Protection Board of India (DPBI) following an inquiry.
---
Schedule of Penalties Under DPDPA
| Violation Description | Relevant Section | Maximum Statutory Penalty |
| :--- | :--- | :--- |
| Failure to implement reasonable security safeguards resulting in a data breach | Section 8(5) |
Up to ₹250 Crore |
| Failure to notify the Board and Data Principals of a personal data breach | Section 8(6) |
Up to ₹200 Crore |
| Non-compliance with children's data obligations (tracking, profiling, VPC) | Section 9 |
Up to ₹200 Crore |
| Failure to fulfill Significant Data Fiduciary (SDF) obligations | Section 10 |
Up to ₹150 Crore |
| General breach of any other provision of the Act or Rules | Residual |
Up to ₹50 Crore |
| Non-compliance with duties by a Data Principal (frivolous complaints) | Section 15 | Up to ₹10,000 |
---
How the Data Protection Board Determines Penalty Amounts
Section 33 of the Act requires the Board to consider multiple mitigating and aggravating factors:
1.
Nature, gravity, and duration of the non-compliance.
2.
Type and nature of personal data affected (e.g. financial data, biometrics, children's data).
3.
Repetitive nature of the violation.
4.
Action taken by the Fiduciary to mitigate the breach and its impact.
5.
Proportionality and financial impact on the business.
---
How Enterprises Can Mitigate Penalty Exposure
1.
Maintain Defensible Proof of Compliance: Maintain immutable, time-stamped logs of all consent events, DSR fulfillments, and security measures.
2.
Implement Zero-Trust Tokenization: Storing sensitive PII in a zero-trust vault reduces breach blast radius, eliminating raw PII exfiltration.
3.
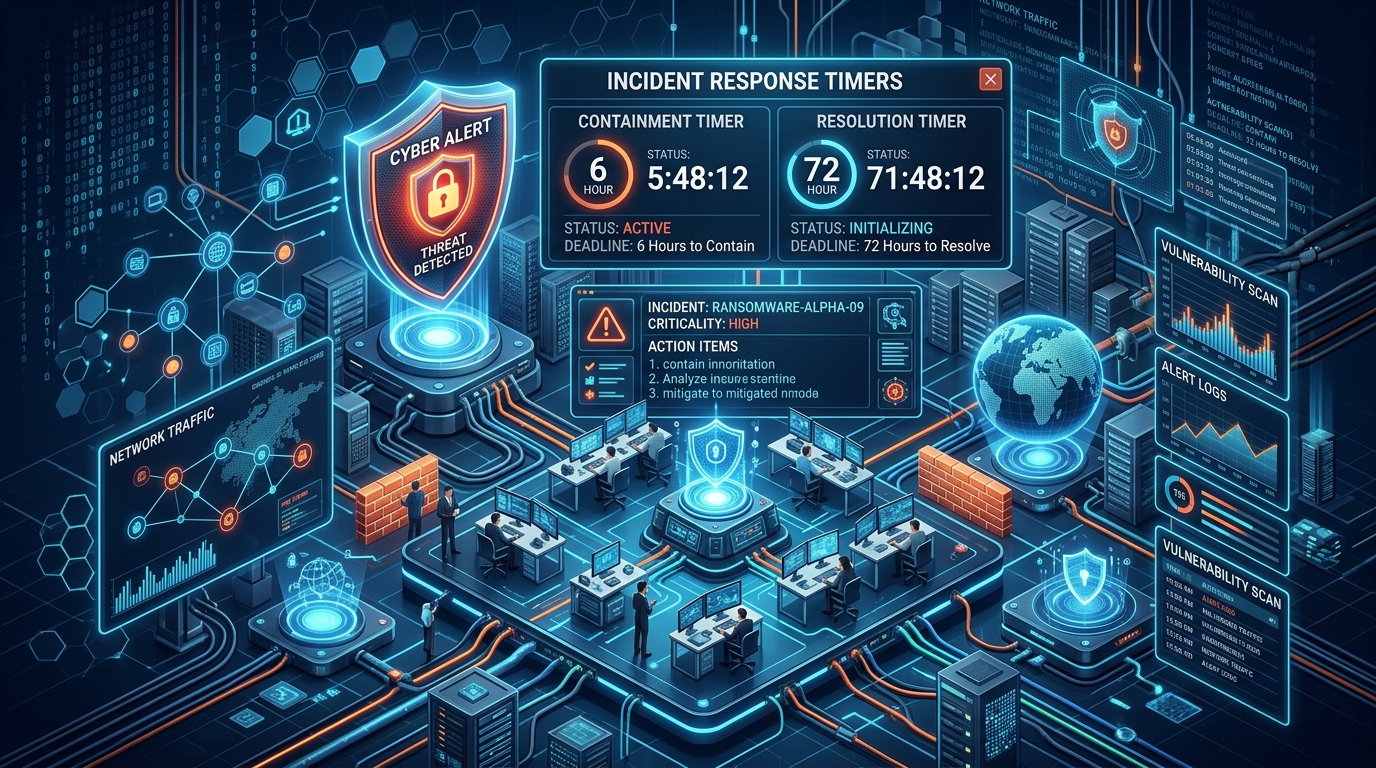
Rapid Incident Escalation: Demonstrating proactive notification within the CERT-In 6-hour and DPBI 72-hour windows significantly mitigates regulatory severity.