Why Section 9 is the Strictest Regime in the DPDP Act
Under the DPDP Act 2023, anyone under
18 years of age is legally classified as a child. This is significantly more stringent than the EU GDPR (age 16) or the US COPPA (age 13). There is no tiered age classification: teenagers, college students under 18, and kindergarteners are subject to the same strict protections.
Violations under Section 9 carry penalties up to
₹200 crore, making child data governance a top-tier operational risk.
---
The 3 Non-Negotiable Rules of Section 9
1. Verifiable Parental Consent (VPC)
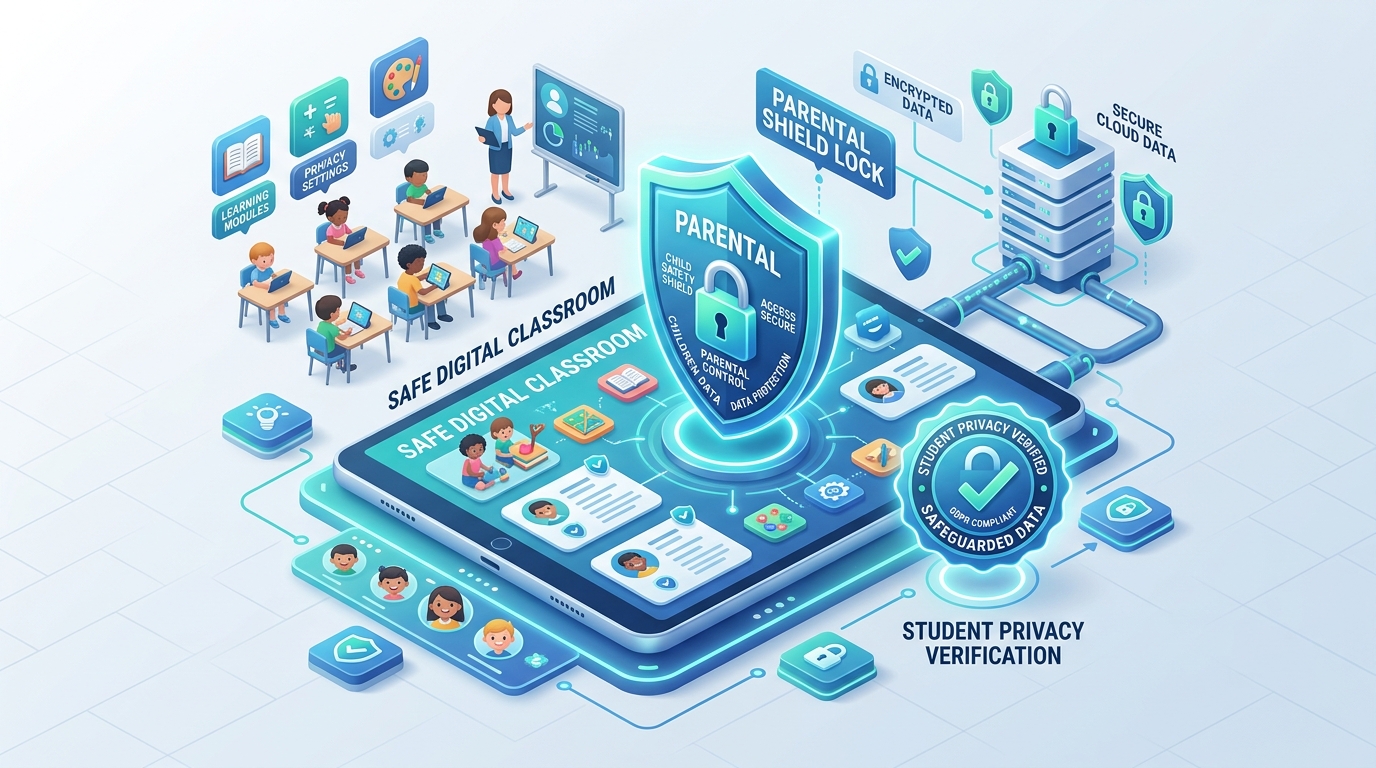
A simple self-declaration checkbox ("I am 18+") is legally invalid. Platforms must implement verifiable parental consent workflows before ingesting any personal data of a minor. Approved mechanisms include:
DigiLocker-based guardian verification
SMS/OTP-authenticated parent account linkage
Tokenized identity verification via government-backed IDs2. Absolute Prohibition on Behavioural Tracking & Targeted Ads
Section 9(3) imposes a complete ban on tracking student/child user behaviour, creating engagement heatmaps, or serving targeted advertisements based on user data.
This ban applies even if the parent gives consent.3. Ban on Processing Likely to Cause Detrimental Effect
Platforms cannot process children's data in any manner that could cause physical or psychological harm, algorithmic addiction, or discriminatory outcome.
---
Architectural Checklist for Tech Teams
Strip tracking pixels (Meta Pixel, Google Tag Manager) from all pages accessed by minors.
Implement purpose-isolated databases for children's learning records.
Provide parent-facing self-service DSR portals for instant access and erasure.