Vicarious Liability under the DPDP Act
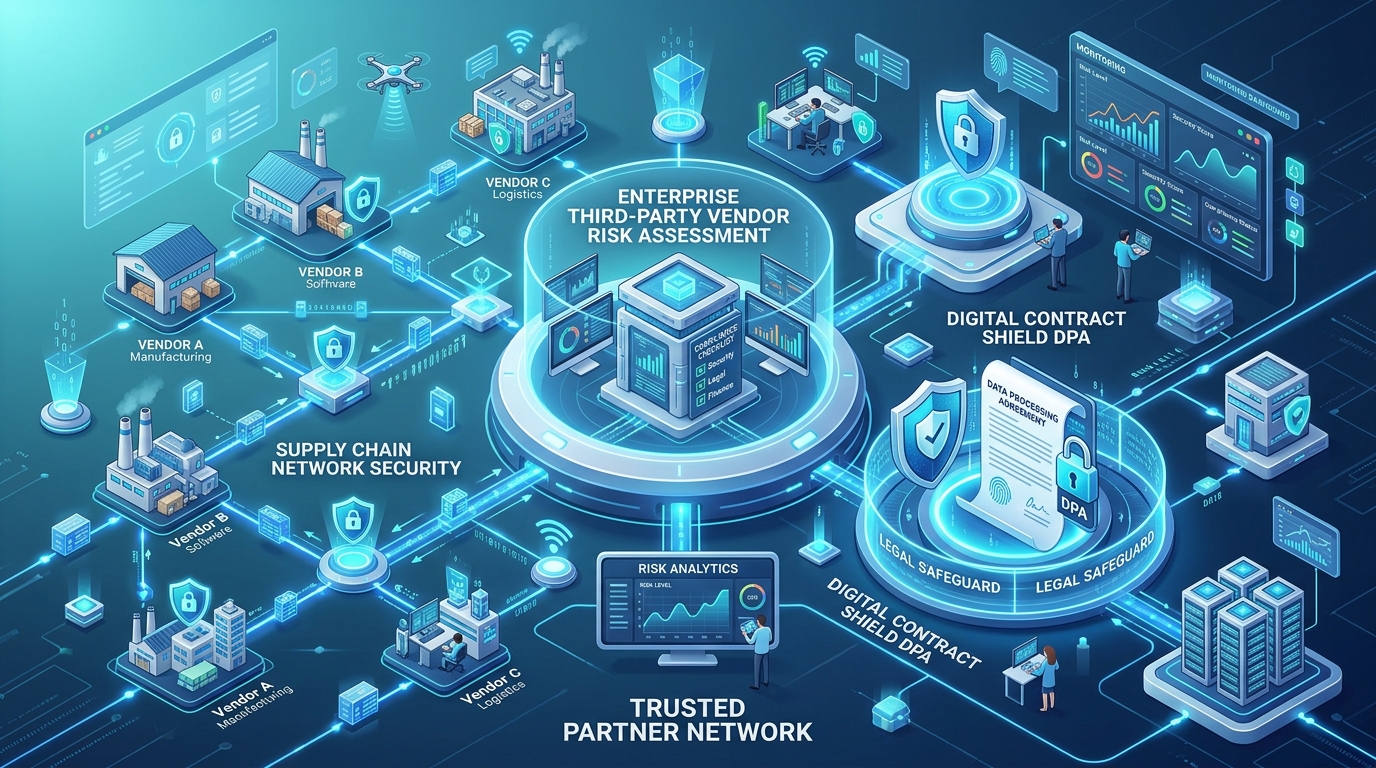
Under Section 8(2) of India's DPDP Act, a Data Fiduciary remains
fully and primarily liable for any breach, misuse, or non-compliance caused by its Data Processors and sub-processors.
If your third-party payment gateway, analytics SDK, cloud host, or outsourced customer support vendor leaks personal data, the Data Protection Board will penalise
your organisation as the Data Fiduciary.
---
4 Mandatory Clauses Every Indian DPA Must Contain
1.
Processing Exclusively on Documented Instructions: The processor cannot use client data to train internal AI models, aggregate market data, or market secondary services.
2.
Mandatory Security Safeguards (Section 8(5)): Explicit requirement for AES-256 encryption, certified SOC 2 / ISO 27001 ISMS controls, and periodic penetration testing.
3.
Sub-Processor Pre-Notification: A requirement that the processor notify and obtain consent from the fiduciary before onboarding new cloud or software vendors.
4.
Post-Termination Data Sanitization: Legally binding obligation to cryptographically erase or return all personal data within 30 days of contract conclusion.
---
Transitioning from Spreadsheets to Continuous Vendor Risk
Sending manual Excel questionnaires once a year does not satisfy regulatory due diligence. PrivacyOS automates vendor onboarding, DPA repository indexing, and dynamic risk scoring across your entire supply chain.