What is DPDPA?
The
Digital Personal Data Protection Act, 2023 (DPDPA) is India's comprehensive national data privacy law enacted by Parliament. It establishes a legally binding framework governing the processing of digital personal data within India, replacing Section 43A of the Information Technology Act, 2000.
DPDPA balances an individual's fundamental right to protect their personal data (recognized in the landmark
Puttaswamy judgment) with the legitimate processing needs of businesses and public entities.
---
Who Does the DPDPA Apply To?
The DPDP Act applies to:
1.
Processing within India: Any processing of digital personal data collected online, or collected offline and digitized subsequently.
2.
Extraterritorial Scope: Processing outside India if it involves offering goods or services to Data Principals located in India.
Every entity deciding the purpose and means of processing is defined as a
Data Fiduciary, while individuals whose data is processed are termed
Data Principals. Unlike Western frameworks, DPDPA provides
no exemption based on business size or turnover—a 5-person startup and a conglomerate share identical statutory obligations.
---
Core Obligations Under the DPDP Act
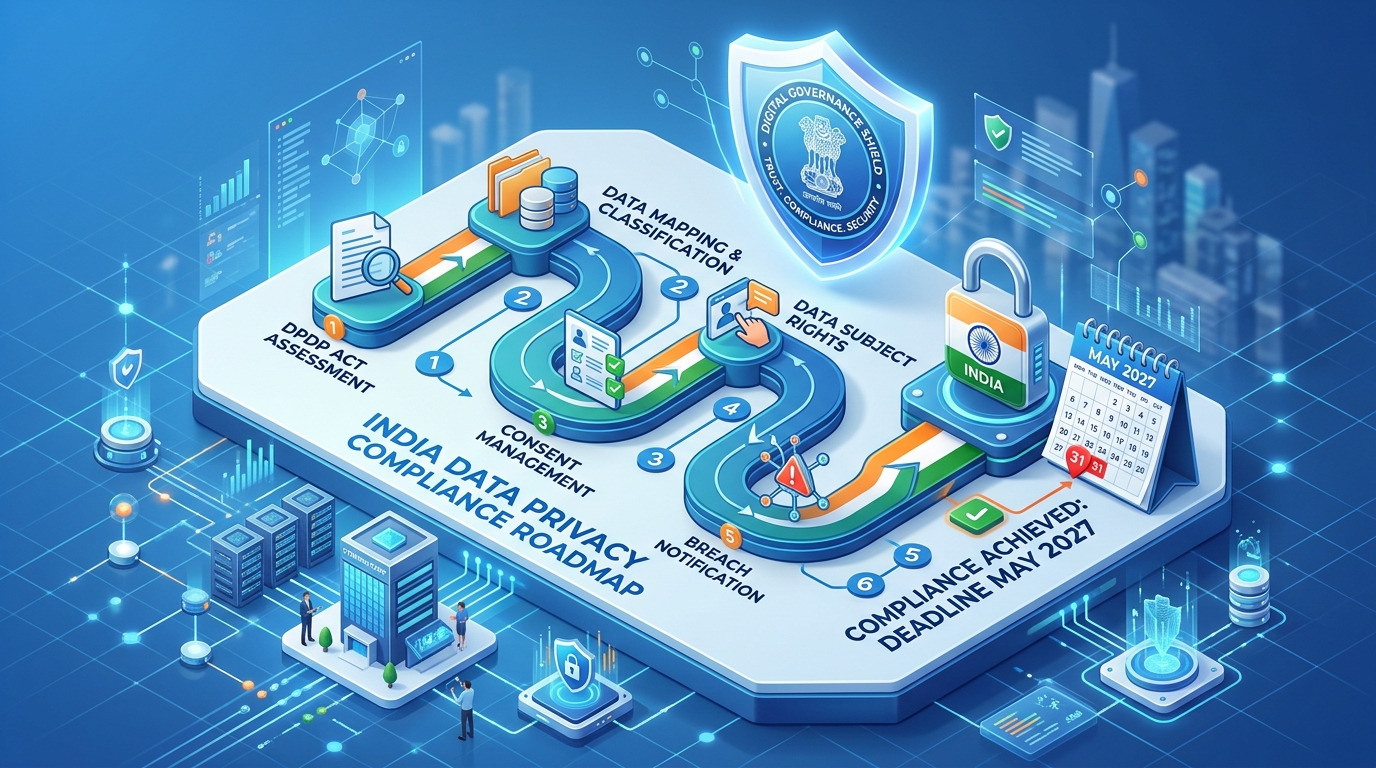
Notice & Consent (Section 5 & 6): Prior to or at the time of request, Data Fiduciaries must present an itemised notice in English or any of the 22 scheduled Indian languages specifying the exact personal data to be processed and its purpose.
Data Principal Rights (Section 11–14): Citizens have statutory rights to access summaries of personal data, correct inaccuracies, erase obsolete records, and nominate representatives.
Mandatory Breach Notification (Section 8(6)): Fiduciaries must notify both the Data Protection Board of India (DPBI) and affected individuals in the event of a personal data breach.
Protection of Children's Data (Section 9): Absolute prohibition on behavioural tracking, targeted advertising, or profiling of individuals under 18 years, accompanied by verifiable parental consent.
Reasonable Security Safeguards (Section 8(5)): Technical and organisational measures, including tokenization, encryption, and role-based access control.---
Compliance Timelines & Next Steps
With the DPDP Rules notified, Indian enterprises must achieve full readiness before
13 May 2027. Beginning with automated data discovery, notice refactoring, and DSR workflow deployment ensures your organization avoids severe statutory penalties.